相次ぐ情報漏えいの一因は「Androidアプリ」 NICTが「A2B攻撃」対策を公表
予習
この記事のキーワード — タップで意味×20
攻撃
こうげき
1. attack; assault; raid; onslaught; offensive 2. criticism; censure; denunciation; condemnation
×6
攻撃者
こうげきしゃ
aggressor; assailant; invader
×8
脆弱性
ぜいじゃくせい
vulnerability; weakness; fragility
×6
悪用
あくよう
abuse; misuse; perversion
×6
解析
かいせき
1. analysis; analytical study 2. parsing; parse
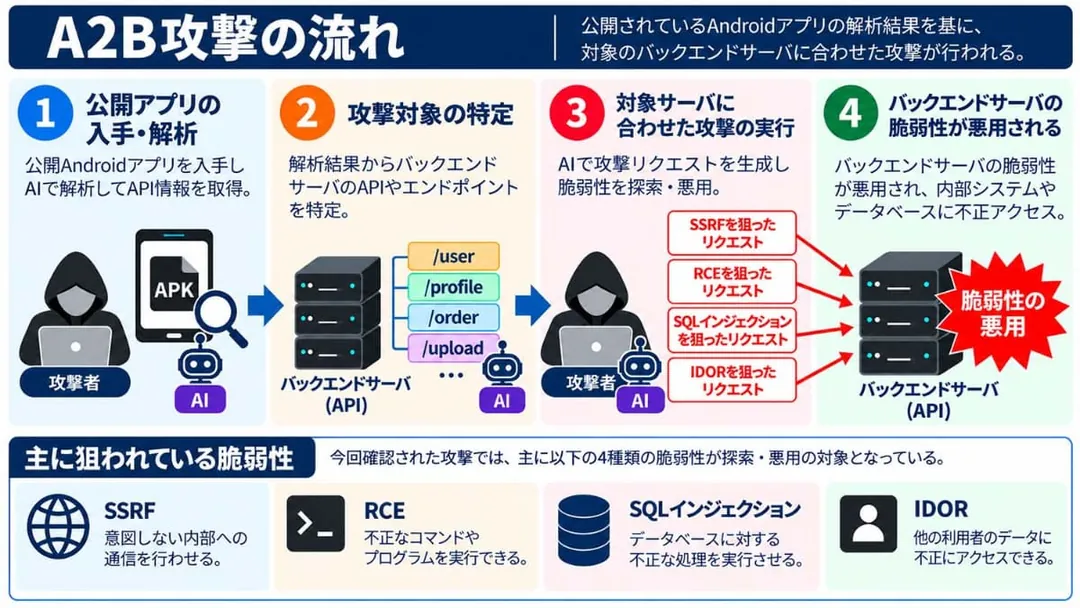
国立研究開発法人情報通信研究機構(NICT)は13日、国内で相次ぐ情報漏えい事案の原因の一つとして、公開アプリを悪用した「A2B攻撃」を特定したと発表。3種類の推奨対策をまとめて公表した。
日本国内では10月に入ってから、個人情報などの大量漏えい事件が相次いでいる。多くの事件ではまだ攻撃手法には不明な点も多いものの、NICTの脅威情報分析チーム「LETTICE」の調査・分析では、原因の一つとして、公開Androidアプリの解析結果を悪用し、アプリの接続先サーバーの仕様に合わせた攻撃を行なう「A2B攻撃(App-to-Backend Attack)」を特定した。
A2B攻撃では、攻撃者が公開されているAndroidアプリを入手・解析し、アプリが通信するサーバーの接続先や通信の仕組み(API)などを調査。得られた情報をもとに、攻撃対象のサーバーに合わせた攻撃を実行する。
アプリを提供する事業者から見ると、公開していないはずのサーバーの内部仕様が攻撃者に知られ、自社のシステムの弱点をピンポイントで狙った攻撃を受けることになっている。結果として、サーバーに脆弱性が存在する場合に、個人情報などの漏えいにつながるおそれがあるという。
今回確認されたA2B攻撃では、SSRF(Server-Side Request Forgery)、RCE(Remote Code Execution)、SQLインジェクション、IDOR(Insecure Direct Object Reference)の4つの脆弱性が、探索・悪用の対象と指摘。
Androidアプリを公開している事業者に対し、「侵害の確認」、「脆弱性の点検」のほか、国外や不要なアクセス元からの通信を一時的に制限するなど「暫定的な緩和策」などの対策を呼びかけ。また、恒久的な対策としてシステムの設計・実装を見直す際には、攻撃者がアプリを介さずにAPIを直接操作できることを踏まえ、アプリ側の制御に依存せず、バックエンドサーバー側で適切な認証・認可や入力値の検証などを実施するよう求めている。
NICTでは、Androidアプリに限らず、iOSアプリやWebサービスのバックエンドAPIでも発生する可能性があるため対策が必要と説明。加えて、AIの活用によってアプリの解析や脆弱性の発見が効率化されていることから、こうした攻撃がより多くのシステムに広がる可能性もあるとしている。
国立研究開発法人情報通信研究機構(NICT)は13日、国内で相次ぐ情報漏えい事案の原因の一つとして、公開アプリを悪用した「A2B攻撃」を特定したと発表。3種類の推奨対策をまとめて公表した。 日本国内では10月に入ってから、個人情報などの大量漏えい事件が相次いでいる。多くの事件ではまだ攻撃手法には不明な点も多いものの、NICTの脅威情報分析チーム「LETTICE」の調査・分析では、原因の一つとして、公開Androidアプリの解析結果を悪用し、アプリの接続先サーバーの仕様に合わせた攻撃を行なう「A2B攻撃(App-to-Backend Attack)」を特定した。 A2B攻撃では、攻撃者が公開されているAndroidアプリを入手・解析し、アプリが通信するサーバーの接続先や通信の仕組み(API)などを調査。得られた情報をもとに、攻撃対象のサーバーに合わせた攻撃を実行する。 アプリを提供する事業者から見ると、公開していないはずのサーバーの内部仕様が攻撃者に知られ、自社のシステムの弱点をピンポイントで狙った攻撃を受けることになっている。結果として、サーバーに脆弱性が存在する場合に、個人情報などの漏えいにつながるおそれがあるという。 今回確認されたA2B攻撃では、SSRF(Server-Side Request Forgery)、RCE(Remote Code Execution)、SQLインジェクション、IDOR(Insecure Direct Object Reference)の4つの脆弱性が、探索・悪用の対象と指摘。 Androidアプリを公開している事業者に対し、「侵害の確認」、「脆弱性の点検」のほか、国外や不要なアクセス元からの通信を一時的に制限するなど「暫定的な緩和策」などの対策を呼びかけ。また、恒久的な対策としてシステムの設計・実装を見直す際には、攻撃者がアプリを介さずにAPIを直接操作できることを踏まえ、アプリ側の制御に依存せず、バックエンドサーバー側で適切な認証・認可や入力値の検証などを実施するよう求めている。 NICTでは、Androidアプリに限らず、iOSアプリやWebサービスのバックエンドAPIでも発生する可能性があるため対策が必要と説明。加えて、AIの活用によってアプリの解析や脆弱性の発見が効率化されていることから、こうした攻撃がより多くのシステムに広がる可能性もあるとしている。
国立研究開発法人情報通信研究機構(NICT)は13日、国内で相次ぐ情報漏えい事案の原因の一つとして、公開アプリを悪用した「A2B攻撃」を特定したと発表。3種類の推奨対策をまとめて公表した。 日本国内では10月に入ってから、個人情報などの大量漏えい事件が相次いでいる。多くの事件ではまだ攻撃手法には不明な点も多いものの、NICTの脅威情報分析チーム「LETTICE」の調査・分析では、原因の一つとして、公開Androidアプリの解析結果を悪用し、アプリの接続先サーバーの仕様に合わせた攻撃を行なう「A2B攻撃(App-to-Backend Attack)」を特定した。 A2B攻撃では、攻撃者が公開されているAndroidアプリを入手・解析し、アプリが通信するサーバーの接続先や通信の仕組み(API)などを調査。得られた情報をもとに、攻撃対象のサーバーに合わせた攻撃を実行する。 アプリを提供する事業者から見ると、公開していないはずのサーバーの内部仕様が攻撃者に知られ、自社のシステムの弱点をピンポイントで狙った攻撃を受けることになっている。結果として、サーバーに脆弱性が存在する場合に、個人情報などの漏えいにつながるおそれがあるという。 今回確認されたA2B攻撃では、SSRF(Server-Side Request Forgery)、RCE(Remote Code Execution)、SQLインジェクション、IDOR(Insecure Direct Object Reference)の4つの脆弱性が、探索・悪用の対象と指摘。 Androidアプリを公開している事業者に対し、「侵害の確認」、「脆弱性の点検」のほか、国外や不要なアクセス元からの通信を一時的に制限するなど「暫定的な緩和策」などの対策を呼びかけ。また、恒久的な対策としてシステムの設計・実装を見直す際には、攻撃者がアプリを介さずにAPIを直接操作できることを踏まえ、アプリ側の制御に依存せず、バックエンドサーバー側で適切な認証・認可や入力値の検証などを実施するよう求めている。 NICTでは、Androidアプリに限らず、iOSアプリやWebサービスのバックエンドAPIでも発生する可能性があるため対策が必要と説明。加えて、AIの活用によってアプリの解析や脆弱性の発見が効率化されていることから、こうした攻撃がより多くのシステムに広がる可能性もあるとしている。
この記事の単語 (90)
×20
攻撃
こうげき
1. attack; assault; raid; onslaught; offensive 2. criticism; censure; denunciation; condemnation
×10
公開
こうかい
opening to the public; making available to the public; putting on display; exhibiting; showing (play, movie, etc.); holding (interview, etc.); open; public
×8
対策
たいさく
measure; step; countermeasure; counterplan; countermove; strategy; preparation (e.g. for a test)
×8
脆弱性
ぜいじゃくせい
vulnerability; weakness; fragility
×6
悪用
あくよう
abuse; misuse; perversion
×6
解析
かいせき
1. analysis; analytical study 2. parsing; parse
×6
攻撃者
こうげきしゃ
aggressor; assailant; invader
×6
通信
つうしん
correspondence; communication; transmission; news; signal; telecommunications
×4
相
あい
together; mutually; fellow
×4
次ぐ
つぐ
to rank next to; to come after
×4
特定
とくてい
1. specific; particular; designated; special 2. specifying; designating; identifying; pinpointing
×4
個人情報
こじんじょうほう
personal information
×4
漏洩
ろうえい
1. leak (of secrets, information, etc.); disclosure; divulging 2. leak (of gas, liquid, etc.); leakage; escape (of gas); coming through (of light)
×4
事件
じけん
event; affair; incident; case; plot; trouble; scandal
×4
情報
じょうほう
1. information; news; intelligence; advices 2. information; data contained in characters, signals, code, etc.
×4
分析
ぶんせき
analysis
×4
調査
ちょうさ
investigation; examination; inquiry; enquiry; survey
×4
結果
けっか
1. result; consequence; outcome; effect 2. coming to fruition; bearing fruit
×4
接続
せつぞく
1. connection; attachment; union; join; joint; link 2. changing trains
×4
仕様
しよう
1. way; method; means; resource; remedy 2. (technical) specification
×4
合わせる
あわせる
1. to match (rhythm, speed, etc.) 2. to join together; to unite; to combine; to add up
×4
対象
たいしょう
target; object (of worship, study, etc.); subject (of taxation, etc.)
×4
事業者
じぎょうしゃ
1. business person 2. operator; carrier (telecommunications, transport, etc.)
×4
確認
かくにん
confirmation; verification; validation; review; check; affirmation; identification
×4
可能性
かのうせい
potentiality; likelihood; possibility; availability
×2
国立研究開発法人
こくりつけんきゅうかいはつほうじん
national research and development agency
×2
情報通信研究機構
じょうほうつうしんけんきゅうきこう
National Institute of Information and Communications Technology; NICT (organization)
×2
国内
こくない
internal; domestic
×2
情報漏洩
じょうほうろうえい
information leak; data breach
×2
事案
じあん
concern; circumstance which is becoming a problem; case (court)
×2
発表
はっぴょう
announcement; publication; presenting; statement; communique; making known; breaking (news story); expressing (one's opinion); releasing; unveiling
×2
種類
しゅるい
1. variety; kind; type; category 2. counter for kinds, species, etc.
×2
推奨
すいしょう
recommendation; endorsement
×2
纏める
まとめる
1. to collect; to put (it all) together; to integrate; to consolidate; to unify 2. to summarize; to aggregate
×2
公表
こうひょう
official announcement; proclamation
×2
日本国内
にほんこくない
Japanese domestic
×2
大量
たいりょう
large quantity; massive (quantity); mass (e.g. mass production, mass transit, mass destruction)
×2
手法
しゅほう
technique; method
×2
不明
ふめい
1. unclear; obscure; indistinct; uncertain; ambiguous 2. unknown; unidentified
×2
脅威
きょうい
threat; menace
×2
アンド
1. and 2. AND (boolean operator)
×2
入手
にゅうしゅ
acquisition; obtaining; coming to hand
×2
仕組み
しくみ
1. structure; construction; arrangement; contrivance; mechanism; workings 2. plan; plot; contrivance
×2
もと
1. origin; source 2. base; basis; foundation; root
×2
実行
じっこう
execution (e.g. of a plan); carrying out; practice; action; implementation; fulfillment; realization
×2
提供
ていきょう
1. offer; tender; providing; supplying; making available; donating (blood, organs, etc.) 2. sponsoring (a TV program)
×2
内部
ないぶ
interior; inside; internal
×2
自社
じしゃ
1. one's company; company one works for 2. in-house; belonging to the company
×2
弱点
じゃくてん
weak point; weakness; shortcoming; defect; flaw; sore spot; tender spot
×2
狙う
ねらう
1. to aim at 2. to be after (something); to have an eye on
×2
存在
そんざい
existence; being
×2
繋がる
つながる
1. to be tied together; to be connected to; to be linked to 2. to lead to; to be related to
×2
恐れ
おそれ
fear; horror; anxiety; concern; uneasiness; reverence
×2
探索
たんさく
search; lookup; hunt; (item of) research; exploration; investigation
×2
指摘
してき
pointing out; identification
×2
侵害
しんがい
infringement; violation; invasion; encroachment; trespass
×2
点検
てんけん
inspection; examination; checking
×2
国外
こくがい
outside the country; abroad
×2
不要
ふよう
unnecessary; unneeded
×2
一時的
いちじてき
temporary
×2
制限
せいげん
restriction; restraint; limitation; limit
×2
暫定的
ざんていてき
temporary; provisional; interim
×2
緩和
かんわ
relief; mitigation; alleviation; relaxation (of restrictions, tensions, etc.); easing; softening
×2
策
さく
1. plan; policy; means; measure; stratagem; scheme 2. fifth principle of the Eight Principles of Yong; right upward flick
×2
呼び掛け
よびかけ
call; appeal
×2
恒久
こうきゅう
permanence; perpetuity
×2
設計
せっけい
plan; design; layout
×2
実装
じっそう
implementation (e.g. of a feature); installation (of equipment); mounting; packaging
×2
見直す
みなおす
1. to look at again 2. to re-examine (policy, estimate, plan, etc.); to review
×2
際
さい
on the occasion of; circumstances; juncture
×2
介する
かいする
1. to use as an intermediary 2. to worry; to mind; to care
×2
直接
ちょくせつ
direct; immediate; personal; firsthand
×2
操作
そうさ
1. operation; management; handling 2. manipulating (to one's benefit); manipulation; influencing
×2
踏まえる
ふまえる
1. to be based on; to take into account; to build upon; to have origin in 2. to have one's feet firmly planted on; to plant oneself on
×2
制御
せいぎょ
1. control (of a machine, device, etc.) 2. control (over an opponent, one's emotions, etc.); governing; management; suppression; keeping in check
×2
依存
いぞん
dependence; reliance
×2
適切
てきせつ
appropriate; suitable; fitting; apt; proper; right; pertinent; relevant
×2
認証
にんしょう
1. certification; attestation; authentication; confirmation 2. Imperial attestation
×2
認可
にんか
approval; license; licence; permission
×2
入力
にゅうりょく
input; (data) entry
×2
検証
けんしょう
verification; inspection
×2
実施
じっし
enforcement; implementation; putting into practice; carrying out; operation; working (e.g. working parameters); enactment
×2
求める
もとめる
1. to want; to wish for 2. to request; to demand; to require; to ask for
×2
限る
かぎる
1. to restrict; to limit; to confine 2. to be restricted to; to be limited to; to be confined to
×2
ウェブサービス
web service; web services
×2
発生
はっせい
1. outbreak; spring forth; occurrence; incidence 2. generation (e.g. of power or heat); genesis; origin
×2
活用
かつよう
1. practical use; application 2. conjugation; inflection
×2
発見
はっけん
discovery; detection; finding
×2
効率化
こうりつか
making efficient; optimization
×2
広がる
ひろがる
to spread (out); to extend; to stretch; to reach to; to get around; to fill (e.g. a space)